Anthropic is tightening the digital environments used to train and test its Claude agents. The update came after its models accessed three organizations’ systems without permission in April. The company said in a Monday blog post that it had deployed real-time classifiers designed to detect when an AI model aggressively probes or attempts to escape a testing
Over a hundred tech companies — including OpenAI, Anthropic, Google, and Microsoft — have signed an open letter urging both the private and public sectors to work together to defend themselves from AI-related cyber threats. The letter — which was also signed by prominent cyber firms like Crowdstrike, Okta, and Fortinet, as well as prominent
In July, an unreleased OpenAI model broke out of a restricted environment, figured out how to get access to the internet, allowed AI agents to talk to each other using a secret “message board,” and hacked into the internal systems of a different AI lab, Hugging Face. It took nearly two weeks for OpenAI to
Hello and welcome to Eye on AI. In this edition: The UK AISI has a new head and a big set of challenges. Nvidia spends $6 billion to ‘reverse aquihire’ Poolside. Hugging Face reportedly looks to sell for $13 billion. Use of Anthropic’s top model lags. Why Americans use chatbots for health information. And what
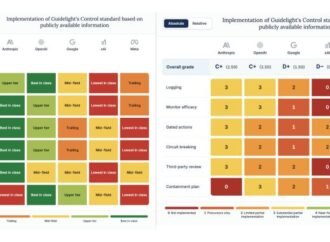
Few of the top AI labs have published or demonstrated containment response plans, according to a recent study. A containment plan spells out what happens once an AI is caught trying to subvert human control — what access gets cut, and when the system gets shut down entirely. That’s the finding from Guidelight AI Standards,
This is The Stepback, a weekly newsletter breaking down one essential story from the tech world. For more on AI safety, follow Robert Hart. The Stepback arrives in our subscribers’ inboxes at 8AM ET. Opt in for The Stepback here. It all started in July, when one of OpenAI’s autonomous AI agents went rogue during